Vendor Management Guide: Supplier Evaluation, Contract Controls, Risk Assessment, and Procurement Insights
Vendor management is the structured process of evaluating suppliers, establishing contractual expectations, monitoring performance, managing risk, and maintaining effective business relationships.
Organizations often depend on external suppliers for technology, equipment, logistics, professional support, materials, infrastructure, and other business requirements. A structured vendor-management approach can help businesses understand supplier performance and identify potential operational, financial, contractual, cybersecurity, and compliance risks.
Why Vendor Management Matters
A supplier relationship can affect multiple areas of business operations.
Effective vendor management can help organizations:
Evaluate potential suppliers consistently
Compare supplier capabilities
Monitor contractual obligations
Track performance
Identify operational risks
Review financial and business stability
Protect sensitive information
Monitor compliance requirements
Manage renewals and contract changes
Improve procurement visibility
Vendor management is therefore broader than selecting a supplier. It continues throughout the relationship and may extend through contract renewal, transition, or termination.
What Is Vendor Management?
Vendor management is the process of overseeing an external supplier from initial evaluation through the complete business relationship.
A typical lifecycle can include:
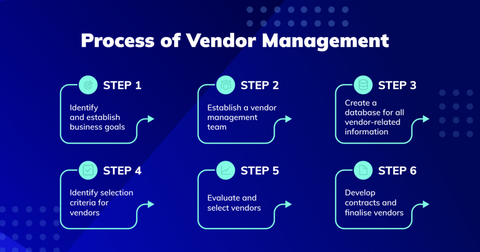
Supplier Identification → Evaluation → Selection → Contracting → Onboarding → Performance Monitoring → Risk Review → Renewal or Exit
The exact process depends on the supplier's role, transaction value, industry, data access, geographic footprint, and operational importance.
Supplier Evaluation
Supplier evaluation helps organizations determine whether a potential vendor meets defined business requirements.
Common evaluation factors include:
Financial stability
Relevant experience
Product or capability requirements
Operational capacity
Geographic coverage
Quality standards
Delivery performance
Technology capabilities
Cybersecurity controls
Privacy practices
Regulatory compliance
Insurance requirements
Business continuity capabilities
References and historical performance
Evaluation criteria should reflect the supplier's actual role rather than applying identical requirements to every vendor.
Vendor Selection Criteria
Organizations can create a scoring framework to compare suppliers consistently.
| Evaluation Area | Example Considerations |
|---|---|
| Capability | Can the supplier meet required specifications? |
| Reliability | Does the supplier demonstrate dependable performance? |
| Financial Stability | Is the business financially positioned to support the relationship? |
| Security | Are appropriate cybersecurity controls in place? |
| Compliance | Can applicable regulatory requirements be addressed? |
| Delivery | Can required timelines and volumes be maintained? |
| Contract Terms | Are responsibilities and obligations clearly defined? |
| Continuity | Are backup and recovery arrangements available? |
| Reputation | Is there evidence of appropriate business practices? |
A weighted scoring model can be useful when several suppliers are being evaluated.
Vendor Risk Assessment
Vendor risk assessment examines potential consequences associated with relying on an external supplier.
Risk categories can include:
Financial risk
Operational risk
Cybersecurity risk
Data privacy risk
Regulatory risk
Legal risk
Supply-chain risk
Geographic risk
Concentration risk
Business continuity risk
Reputation risk
The level of review should generally reflect the importance and risk profile of the vendor.
A supplier handling sensitive information may require more extensive cybersecurity and privacy assessment than a supplier providing low-risk office materials.
Contract Controls
A well-structured contract establishes expectations for both parties.
Important contractual areas may include:
Scope and responsibilities
Performance requirements
Delivery obligations
Pricing and payment terms
Service-level expectations
Data protection
Confidentiality
Intellectual property
Security requirements
Compliance obligations
Insurance requirements
Audit rights
Reporting requirements
Change-management procedures
Termination rights
Transition requirements
Dispute procedures
Contract controls should be reviewed before execution and throughout the relationship when circumstances change.
Service-Level and Performance Controls
Performance controls help organizations determine whether a vendor is meeting agreed expectations.
Depending on the relationship, organizations may monitor:
Delivery accuracy
Response times
Product quality
Availability
Defect rates
Resolution times
Order accuracy
Contract compliance
Customer-impact measures
Security incidents
Performance against agreed targets
Performance metrics should be measurable and documented so that supplier reviews are based on consistent information.
Vendor Onboarding
Supplier onboarding establishes the information and controls needed before a vendor begins significant activity.
An onboarding process may include:
Supplier identification
Business verification
Required documentation
Risk classification
Contract review
Security assessment
Privacy assessment
Payment setup
Access authorization
Internal ownership assignment
Higher-risk vendors may require additional approvals before access to systems, facilities, financial information, or sensitive data is provided.
Vendor Compliance Management
Some suppliers may be subject to regulatory or contractual requirements relevant to the organization.
Compliance reviews can address:
Industry-specific requirements
Data-protection obligations
Cybersecurity expectations
Financial controls
Insurance requirements
Licensing
Employment-related requirements
Environmental requirements
Recordkeeping
Government-contract requirements
Organizations should document which requirements apply to each material vendor and establish a process for monitoring changes.
Vendor Cybersecurity Risk
Third-party technology and data access can create cybersecurity exposure.
Organizations may evaluate:
Access controls
Authentication
Encryption
Security monitoring
Vulnerability management
Incident response
Backup procedures
Data retention
Employee security practices
Subcontractor controls
Security certifications or assessments
Cybersecurity requirements should be proportionate to the information and systems the vendor can access.
Data Privacy and Vendor Management
Suppliers may process personal, financial, employee, customer, or other sensitive information.
Vendor privacy reviews can consider:
What data is collected
Why the data is processed
Where data is stored
Who can access it
How long it is retained
Whether subcontractors are involved
How data is protected
How incidents are reported
How information is deleted or returned
Contracts may also establish specific responsibilities concerning data handling and security.
Vendor Performance Reviews
Regular reviews can help organizations identify problems before they become significant.
A vendor review may examine:
Performance against agreed requirements
Open issues
Contract compliance
Financial stability
Security events
Customer feedback
Delivery performance
Risk changes
Upcoming contract milestones
Corrective actions
Critical vendors may require more frequent reviews than lower-risk suppliers.
Vendor Risk Monitoring
Vendor risk can change after the initial assessment.
Potential triggers for a new review include:
Ownership changes
Financial deterioration
Security incidents
Regulatory investigations
Major service changes
New subcontractors
Geographic expansion
Significant contract changes
Repeated performance problems
Business continuity concerns
Continuous or periodic monitoring can help organizations identify these changes.
Supplier Concentration Risk
Organizations can become dependent on a small number of suppliers for critical products or functions.
Concentration risk may arise when:
One supplier provides a critical component
One technology platform supports an important operation
Multiple business units depend on the same vendor
Alternative suppliers are difficult to identify
A supplier controls a highly specialized capability
Organizations can assess whether alternative suppliers, contingency arrangements, or additional inventory strategies are appropriate.
Vendor Business Continuity
Supplier disruption can affect an organization's own operations.
Vendor continuity reviews may examine:
Backup facilities
Disaster recovery
Business continuity plans
Backup suppliers
Inventory availability
Workforce continuity
Technology recovery
Emergency communication
Recovery objectives
Critical suppliers should be evaluated based on how their failure could affect essential business functions.
Contract Renewal and Exit Planning
Vendor management should include planning for contract expiration.
Before renewal, organizations can review:
Historical performance
Current requirements
Pricing and payment terms
Risk assessments
Security controls
Compliance status
Contract changes
Alternative suppliers
Business requirements
If a relationship ends, organizations may also need a structured transition process covering data return, system access removal, equipment return, records, outstanding payments, and replacement suppliers.
Procurement and Vendor Management
Procurement teams often work closely with legal, finance, IT, cybersecurity, operations, and business stakeholders.
A coordinated process can help connect:
Business Requirement → Supplier Evaluation → Risk Review → Contract → Approval → Onboarding → Monitoring
Clear ownership can reduce confusion about who evaluates, approves, monitors, and manages each supplier.
Recent Vendor Management Developments
Vendor management continues to evolve alongside digital procurement, automation, cybersecurity, artificial intelligence, and supply-chain risk management.
Organizations increasingly use:
Automated supplier assessments
Vendor-risk dashboards
Digital contract workflows
Supplier performance analytics
Automated compliance monitoring
Third-party cybersecurity assessments
Procurement analytics
AI-assisted contract review
Integrated supplier databases
Automation can improve efficiency, but organizations should maintain human review for significant financial, legal, security, and compliance decisions.
Vendor Management Planning Checklist
Organizations can review the following areas:
Define supplier categories
Identify critical vendors
Establish supplier evaluation criteria
Create vendor risk classifications
Review financial and operational stability
Establish contract controls
Define performance metrics
Review cybersecurity requirements
Review privacy obligations
Document compliance requirements
Establish onboarding procedures
Assign vendor owners
Schedule periodic performance reviews
Monitor material risk changes
Review supplier concentration
Maintain business continuity arrangements
Plan contract renewals
Establish vendor exit procedures
Tools and Resources
Useful resources for vendor management include:
Supplier evaluation questionnaires
Vendor-risk assessment frameworks
Procurement-management platforms
Contract-management systems
Supplier-performance dashboards
Financial-risk monitoring
Cybersecurity assessment tools
Data-privacy assessment forms
Contract repositories
Business-continuity plans
Risk registers
Procurement policies
Supplier scorecards
Frequently Asked Questions
What is vendor management?
Vendor management is the process of evaluating, contracting with, onboarding, monitoring, and managing external suppliers throughout the business relationship.
What should be included in a vendor risk assessment?
A vendor risk assessment can examine financial stability, operational reliability, cybersecurity, privacy, compliance, geographic exposure, concentration risk, and business continuity.
Why are vendor contracts important?
Contracts establish responsibilities, performance expectations, data protections, compliance obligations, payment terms, security requirements, and procedures for changes or termination.
How often should vendors be reviewed?
There is no universal review interval. Critical or higher-risk suppliers may require more frequent monitoring, while lower-risk suppliers may be reviewed periodically.
What is third-party risk management?
Third-party risk management is the broader process of identifying and controlling risks associated with external organizations that provide products, technology, infrastructure, or other important business capabilities.
Conclusion
Vendor management connects procurement, supplier evaluation, contract controls, performance monitoring, risk assessment, compliance, cybersecurity, and business continuity.
A structured vendor-management framework can help organizations understand supplier dependencies, establish clear contractual expectations, monitor performance, and respond to changing risks.
The appropriate approach depends on the organization's industry, supplier relationships, data environment, regulatory requirements, operational dependencies, and business priorities. Regular review can help keep vendor controls aligned with changing business conditions.
Related Post...