Industrial Plant Cybersecurity (OT Security): An Overview of Controls, Monitoring and Risks
Industrial plant cybersecurity, often called OT security, focuses on protecting the operational technology used to monitor and control industrial processes.
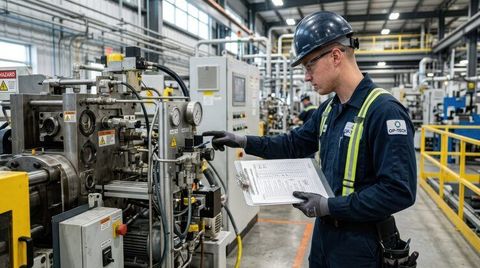
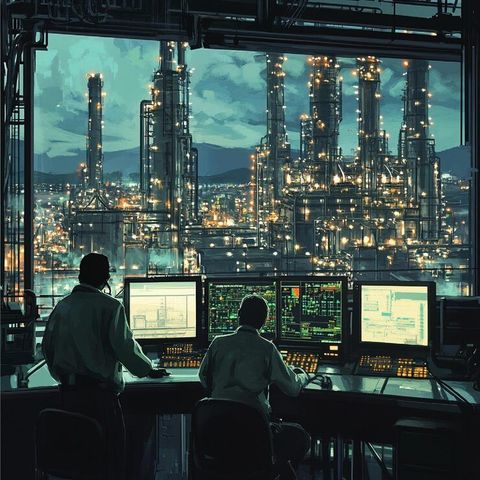
Unlike ordinary office networks, OT environments can include programmable logic controllers, distributed control systems, supervisory control and data acquisition platforms, industrial computers, sensors, drives, and safety systems. These technologies support manufacturing, energy, water treatment, transportation, chemical processing, and other critical operations.
As industrial facilities become more connected, the boundary between information technology (IT) and operational technology (OT) has become less distinct. This connectivity can improve monitoring and coordination, but it also introduces cybersecurity considerations that were less prominent when industrial systems operated in isolated environments.
Context
What Is Industrial Plant Cybersecurity?
Industrial plant cybersecurity is the practice of protecting industrial control environments from unauthorized access, malware, manipulation, data loss, and operational disruption. OT security specifically focuses on systems that interact with physical equipment and industrial processes.
A traditional IT system mainly handles information, applications, communication, and business data. An OT system can influence physical activities such as motor operation, temperature control, pressure regulation, material movement, or electrical distribution. Because of this connection to physical processes, OT security requires attention to both digital and operational risks.
How OT Environments Developed
Industrial control systems were historically designed around reliability, continuous operation, and predictable communication. Many facilities used dedicated networks and specialized hardware that were separated from corporate computing systems.
Modern industrial plants increasingly use Ethernet networks, remote monitoring, cloud-connected applications, industrial Internet of Things devices, and centralized data platforms. These technologies create additional communication paths between industrial assets and external or enterprise environments.
OT security therefore considers the entire industrial environment rather than a single computer. It can involve network architecture, controllers, engineering workstations, human-machine interfaces, sensors, remote connections, software, physical access, and personnel practices.
Common OT Components
Several technologies commonly appear in industrial environments:
- Programmable logic controllers (PLCs) control specific machines or processes.
- Distributed control systems (DCS) coordinate complex continuous processes.
- SCADA systems collect information and supervise geographically distributed equipment.
- Human-machine interfaces (HMIs) allow operators to view process information and interact with controls.
- Industrial network switches and gateways connect equipment and communication segments.
- Engineering workstations are used to configure and maintain control systems.
- Industrial sensors and actuators provide measurements and physical control.
Each component can have different security requirements, operating lifecycles, and communication protocols.
Importance
Protecting Physical Processes
The importance of industrial plant cybersecurity comes from the relationship between digital systems and physical equipment. Unauthorized changes to a controller or process configuration could affect production parameters, equipment behavior, or safety-related operations.
Cybersecurity planning therefore needs to consider consequences beyond data confidentiality. Availability, system integrity, process continuity, and safe operation are also important objectives.
Reducing Operational Disruption
Industrial facilities may depend on interconnected control systems that operate continuously. A cybersecurity incident can create problems ranging from unavailable monitoring information to unexpected equipment behavior or interruption of production activities.
A structured OT security program helps organizations identify critical assets, understand communication paths, monitor unusual activity, and establish procedures for responding to incidents.
Addressing Legacy Technology
Many industrial plants contain equipment that has operated for years or decades. Some older systems may use outdated operating systems, proprietary protocols, or hardware that cannot easily support modern security controls.
Replacing every legacy component is not always practical. Segmentation, controlled access, network monitoring, configuration management, compensating controls, and carefully planned maintenance can form part of a broader approach.
IT and OT Have Different Priorities
| Area | IT Environment | OT Environment |
|---|---|---|
| Main focus | Information and applications | Physical processes and control |
| Availability | Important | Often critical to operations |
| Change approach | Frequent updates may be normal | Changes require careful validation |
| Typical assets | Servers, laptops, databases | PLCs, HMIs, DCS, sensors |
| Main concern | Data and system access | Process integrity and safe operation |
| Maintenance | Often flexible | Frequently coordinated with plant activities |
The distinction does not mean IT and OT should operate independently. Instead, their different requirements need to be considered when designing connections and security controls.
Recent Updates
Greater IT-OT Connectivity
Recent industrial cybersecurity trends from 2024 through 2026 have continued toward greater integration between industrial networks and enterprise systems. Facilities increasingly collect production information for analytics, maintenance planning, energy monitoring, quality management, and operational visibility.
This integration increases the importance of carefully controlled communication between IT and OT environments. Network segmentation, identity controls, secure remote access, and monitoring are increasingly considered as part of industrial architecture.
Increased Use of Network Monitoring
OT network monitoring has become more important as facilities seek greater visibility into industrial communications. Specialized monitoring can identify connected assets, communication patterns, unusual behavior, and unexpected connections.
Passive monitoring is particularly relevant in environments where active scanning could interfere with sensitive equipment. Security teams may therefore use techniques designed to observe industrial traffic without directly changing control devices.
Greater Attention to Remote Access
Remote connectivity has become a major consideration for industrial organizations. Engineers, equipment specialists, maintenance teams, and centralized operations groups may need controlled access to geographically distributed facilities.
Current approaches increasingly emphasize identity verification, limited privileges, session controls, authentication mechanisms, logging, and defined access periods rather than unrestricted network connections.
Cybersecurity and Safety Convergence
Another important trend is greater recognition that cybersecurity and functional safety can influence one another. A cyber incident involving a control system can potentially affect physical operations, while a safety event can influence cybersecurity decisions.
Industrial organizations increasingly evaluate cyber risks alongside process safety, equipment reliability, emergency procedures, and business continuity planning.
Security by Design
New industrial projects increasingly consider cybersecurity during system architecture and procurement rather than treating it solely as a later maintenance activity. Asset inventories, network zoning, authentication, secure configuration, backup planning, and monitoring can be incorporated into the design process.
Laws or Policies
Indian Regulatory Context
In India, industrial cybersecurity is influenced by national cybersecurity policy, sector-specific requirements, information technology regulations, and standards used by individual organizations. Requirements can differ significantly between manufacturing, power, telecommunications, transportation, water, pharmaceuticals, and other sectors.
The Information Technology Act, 2000, together with related rules and subsequent amendments, forms part of India's broader legal framework for electronic systems and cybersecurity. Organizations handling information infrastructure may also need to consider directions and requirements issued by the Indian Computer Emergency Response Team (CERT-In).
Critical Information Infrastructure
India has a framework for protecting critical information infrastructure, particularly where disruption could have significant consequences for national functions. The National Critical Information Infrastructure Protection Centre (NCIIPC) has a role in protecting designated critical information infrastructure.
Industrial organizations that fall within designated sectors or categories may have additional requirements. The exact obligations depend on the nature of the organization and its infrastructure.
Sector-Specific Requirements
Industrial facilities should also consider rules and standards relevant to their particular sector. Electricity-related facilities may encounter requirements associated with the Central Electricity Authority, while environmental and process-related operations may involve authorities such as the Ministry of Environment, Forest and Climate Change and relevant pollution control boards.
International frameworks are also widely referenced in industrial cybersecurity. Examples include the IEC 62443 family for industrial automation and control system security, ISO/IEC 27001 for information security management, and NIST cybersecurity guidance. These frameworks provide structured concepts but do not replace applicable Indian legal requirements.
Tools and Resources
Asset Inventory Platforms
An accurate asset inventory is a fundamental resource for OT security planning. It can record controllers, HMIs, workstations, network devices, communication links, software versions, and other industrial assets.
The inventory can also identify ownership, location, importance, and maintenance information. Keeping these records current helps organizations understand which systems require additional protection.
Network Segmentation Tools
Firewalls, industrial network switches, gateways, and virtual network technologies can help separate different operational zones. Segmentation can reduce unnecessary communication between systems and limit the potential spread of a cybersecurity incident.
The architecture should be designed around actual process requirements rather than simply dividing networks without understanding operational communication.
Security Frameworks and Guidance
Organizations can consult resources such as:
- NIST Cybersecurity Framework and NIST industrial cybersecurity publications
- IEC 62443 standards for industrial automation and control systems
- ISO/IEC 27001 information security guidance
- CERT-In cybersecurity advisories and directions
- NCIIPC guidance for relevant critical infrastructure
- CISA industrial control system cybersecurity resources
- Vendor documentation for specific PLC, SCADA, DCS, and HMI platforms
Backup and Recovery Planning
Backups are another important component of OT security. Relevant information may include controller configurations, HMI projects, engineering files, system images, network configurations, and critical documentation.
Backups should be protected against unauthorized modification and periodically checked for usability. Recovery planning should also account for dependencies between control systems and physical equipment.
FAQs
What is industrial plant cybersecurity?
Industrial plant cybersecurity is the protection of digital systems that monitor and control industrial processes. It covers OT networks, PLCs, SCADA platforms, DCS environments, HMIs, engineering workstations, and related infrastructure.
What does OT security protect?
OT security protects operational technology and the processes connected to it. Its objectives can include maintaining system integrity, controlling access, supporting availability, detecting unusual activity, and reducing risks to physical operations.
Why is industrial plant cybersecurity different from IT security?
Industrial plant cybersecurity must account for physical processes, operational continuity, equipment lifecycles, safety considerations, and specialized control technologies. IT security generally focuses more heavily on information, applications, endpoints, and enterprise computing environments.
What are common OT security measures?
Common measures include asset inventories, network segmentation, controlled remote access, strong authentication, least-privilege access, monitoring, secure configuration, vulnerability management, backups, incident response planning, and personnel awareness.
Which standards are used for OT security?
IEC 62443 is widely associated with industrial automation and control system security. NIST publications, ISO/IEC 27001, and sector-specific guidance can also provide useful frameworks for organizing cybersecurity practices.
Conclusion
Industrial plant cybersecurity, or OT security, addresses cybersecurity risks affecting systems that interact with physical industrial processes. Its scope includes control equipment, networks, software, remote access, monitoring, configuration management, and recovery planning. Recent developments have increased attention to IT-OT connectivity, network visibility, remote access, cybersecurity architecture, and the relationship between cyber risks and operational safety. In India, organizations may need to consider national cybersecurity requirements, sector-specific rules, and recognized technical standards according to their infrastructure and activities.
Related Post...
Vibration Analysis: Insights Into Machinery Monitoring, Sensors, Signals, and Testing
Updated: September 09, 2026
Read More
Industrial Laser Annealing: Explore Basics, Equipment, Methods, and Applications
Updated: September 09, 2026
Read More
Chemical Vapor Deposition (CVD): Principles, Uses and Developments Guide
Updated: September 10, 2026
Read More