Business Continuity Planning Guide: Risk Assessment, Recovery Strategies, and Operations
Business continuity planning is the structured process of preparing an organization to maintain or restore important operations when a disruption occurs.
Disruptions can result from natural disasters, power failures, technology outages, cyber incidents, equipment problems, supply-chain interruptions, facility issues, or other unexpected events.
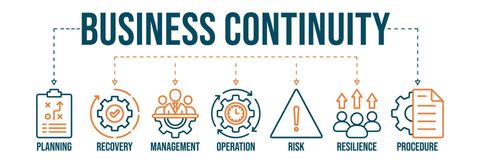
A business continuity program identifies critical activities, evaluates potential disruptions, establishes recovery priorities, and documents strategies for maintaining essential operations.
Business continuity is broader than disaster recovery. Disaster recovery generally focuses on restoring technology, systems, and data, while business continuity addresses the wider operational requirements needed to continue important business functions.
Why Business Continuity Planning Matters
Organizations depend on interconnected employees, technology, facilities, suppliers, information, and infrastructure.
A disruption affecting one area can create consequences across multiple departments.
A continuity program can help organizations:
Identify critical business functions
Assess operational risks
Establish recovery priorities
Document response procedures
Define alternative operating arrangements
Protect important information
Coordinate employees and stakeholders
Reduce disruption to essential activities
Establish recovery objectives
Improve organizational resilience
The objective is not to predict every possible event. Instead, planning should help an organization respond effectively when conditions change unexpectedly.
Business Risk Assessment
Risk assessment is an important starting point for continuity planning.
Organizations can identify potential threats across several categories:
Natural hazards
Cybersecurity incidents
Technology failures
Power interruptions
Facility disruptions
Equipment failures
Supplier interruptions
Transportation problems
Workforce shortages
Utility outages
Financial disruptions
Regulatory or operational changes
Each risk can be evaluated according to its likelihood, potential impact, existing controls, and recovery requirements.
Risk assessments should be reviewed periodically because business processes, technologies, suppliers, facilities, and external conditions can change.
Business Impact Analysis
A business impact analysis (BIA) examines the consequences of losing important business functions.
A BIA may identify:
Critical processes
Required personnel
Supporting technology
Essential information
Important suppliers
Maximum tolerable downtime
Recovery priorities
Financial and operational consequences
The analysis helps organizations determine which processes need the fastest recovery.
For example, a critical payment-processing function may have substantially different recovery requirements from a nonessential administrative reporting process.
Recovery Time and Recovery Point Objectives
Two important continuity concepts are Recovery Time Objective (RTO) and Recovery Point Objective (RPO).
RTO represents the targeted period within which a system or business function should be restored after disruption.
RPO addresses the amount of data loss that may be acceptable based on the point in time to which information needs to be recovered.
These objectives should be established according to business requirements rather than selected solely based on available technology.
Critical systems may require more stringent recovery arrangements than lower-priority applications.
Business Continuity Strategies
Recovery strategies should correspond to the risks and business-impact findings.
Potential approaches include:
Alternative facilities
Organizations may establish alternative locations where critical activities can continue.
Remote operations
Remote-work capabilities can support continuity when a primary facility becomes unavailable, provided employees have appropriate systems and secure access.
Backup systems
Redundant infrastructure, backup applications, and alternate communication systems can reduce dependency on a single technology environment.
Data backup
Regular backups can support information recovery following accidental deletion, system failure, or certain cyber incidents.
Supplier alternatives
Organizations may identify alternate suppliers for critical products or inputs where practical.
Cross-training
Training multiple employees to perform essential responsibilities can reduce dependence on a single individual.
Manual procedures
Documented manual alternatives can provide temporary continuity when automated systems are unavailable.
Disaster Recovery and Business Continuity
Business continuity and disaster recovery are related but distinct.
Business continuity focuses on maintaining critical business functions.
Disaster recovery generally focuses on restoring technology, systems, applications, and data following a disruptive event.
A continuity program may therefore include disaster recovery as one component.
For technology-dependent organizations, disaster recovery planning can address:
Data backup
System restoration
Application recovery
Network recovery
Identity and access management
Cloud infrastructure
Alternate computing environments
Recovery testing
Technology recovery plans should correspond with the recovery requirements identified through the BIA.
Cybersecurity and Business Continuity
Cyber incidents can create significant continuity challenges.
A ransomware event, unauthorized access incident, data compromise, or major technology failure can affect both information and business operations.
Continuity planning should therefore consider:
Backup integrity
Recovery credentials
Network segmentation
Incident-response coordination
Alternative communication channels
Critical application dependencies
Vendor access
Recovery testing
Cyber incident escalation
Backups should not automatically be assumed to be sufficient. Organizations should periodically verify that important data can actually be restored and that recovery procedures work as expected.
Supply-Chain Continuity
Business operations may depend on suppliers, logistics providers, technology providers, utilities, and other external organizations.
Supply-chain continuity planning can identify:
Critical suppliers
Single-source dependencies
Alternative suppliers
Geographic concentration
Supplier recovery capabilities
Contractual continuity provisions
Important subcontractors
Inventory requirements
Vendor continuity information can be incorporated into broader enterprise risk assessments.
This is particularly important where disruption to one supplier could affect several critical business processes.
Continuity Planning for Employees
People are an essential component of business continuity.
Plans may address:
Emergency communication
Employee contact information
Remote-work capabilities
Cross-training
Backup responsibilities
Critical personnel
Workplace safety
Temporary staffing arrangements
Employee access to essential systems
Organizations should ensure that employees understand their responsibilities before a disruption occurs.
A continuity plan that exists only as a document but has never been communicated or tested may be difficult to execute during an actual event.
Business Continuity Testing
Testing helps identify weaknesses before a major disruption occurs.
Common exercises include:
Tabletop exercises: Participants discuss how they would respond to a hypothetical event.
Walkthroughs: Teams review procedures step by step.
Simulation exercises: Participants work through a more realistic scenario.
Technical recovery testing: Technology teams test backup restoration and system recovery.
Communication testing: Organizations verify that emergency communication channels and contact information function as expected.
Testing should produce documented findings and corrective actions.
Business Continuity Documentation
A continuity program may contain several types of documentation.
Examples include:
Business continuity policy
Business impact analysis
Risk assessment
Recovery procedures
Emergency contact lists
Crisis communication procedures
Technology recovery plans
Supplier continuity information
Alternative-site procedures
Testing records
Corrective-action plans
Documents should be maintained so that employees can access the information they need during an actual disruption.
Sensitive information should also be protected through appropriate access controls.
Recent Developments in Business Continuity
Business continuity planning is increasingly connected with cybersecurity, third-party risk, cloud infrastructure, remote operations, and operational resilience.
Organizations are moving beyond facility-focused disaster planning toward broader assessments of interconnected business dependencies.
Cloud applications and distributed workforces can improve flexibility, but they also introduce dependencies on internet connectivity, identity systems, cloud providers, telecommunications, and third-party platforms.
AI-based systems are creating additional continuity considerations because organizations may become dependent on external models, data pipelines, APIs, and technology providers.
Laws, Standards, and U.S. Compliance Considerations
Business continuity requirements depend on the organization's industry and activities.
Certain sectors may have specific regulatory expectations concerning emergency preparedness, information protection, records, operational resilience, or recovery planning.
Organizations may also use recognized frameworks and standards to structure continuity programs.
NIST: NIST provides cybersecurity and risk-management resources that can support continuity and resilience planning.
FEMA: FEMA provides preparedness resources for organizations addressing emergencies and disasters.
ISO 22301: ISO 22301 is an international standard focused on business continuity management systems.
Organizations should determine which legal, contractual, regulatory, and industry requirements apply to their specific operations rather than assuming that one continuity framework satisfies every obligation.
Tools and Resources
Useful continuity-planning resources include:
Business impact analysis templates for identifying critical processes and dependencies
Risk registers for documenting threats, impacts, and mitigation measures
Business continuity management platforms for maintaining plans and exercises
Backup and recovery systems for protecting critical information
Incident-management platforms for coordinating response activities
Emergency notification systems for communicating with employees and stakeholders
Vendor-risk platforms for monitoring critical suppliers
NIST resources for cybersecurity and risk-management planning
FEMA preparedness resources for disaster planning
Organizations should select tools according to their size, industry, technology environment, regulatory obligations, and recovery requirements.
FAQs
1. What is business continuity planning?
Business continuity planning is the process of identifying critical operations and preparing strategies to maintain or restore them following a disruption.
2. What is the difference between business continuity and disaster recovery?
Business continuity focuses on maintaining essential business operations, while disaster recovery generally focuses on restoring technology, systems, applications, and data.
3. What is a business impact analysis?
A business impact analysis identifies important business functions, dependencies, potential consequences of disruption, and recovery priorities.
4. What are RTO and RPO?
RTO is the targeted time for restoring a system or function after disruption. RPO describes the acceptable amount of data loss measured by the point in time to which information must be recovered.
5. How often should a business continuity plan be tested?
Testing frequency should reflect the organization's risks, regulatory requirements, technology changes, and operational complexity. Plans should also be reviewed after significant business or technology changes.
Conclusion
Business continuity planning helps organizations prepare for disruptions by connecting risk assessment, business impact analysis, recovery strategies, technology recovery, supplier planning, employee preparedness, and testing.
An effective program should reflect the organization's actual operations rather than rely on a generic template. Critical dependencies should be identified, recovery priorities should be realistic, and employees should understand their responsibilities.
As organizations become increasingly dependent on technology, cloud systems, suppliers, and interconnected workflows, continuity planning should also address cybersecurity, third-party risk, data recovery, and operational resilience.

Related Post...
Business Continuity Planning Guide: Risk Assessment, Recovery Strategies, and Operations
Updated: September 15, 2026
Read More
Corporate Procurement Guide: Supplier Strategy, Purchasing Workflows, and Compliance
Updated: September 15, 2026
Read More
Business Expense Management Guide: Corporate Spending, Controls, and Financial Workflows
Updated: September 15, 2026
Read More