API Software Guide: Explore Types, Features, Integration, Security & Key Concepts
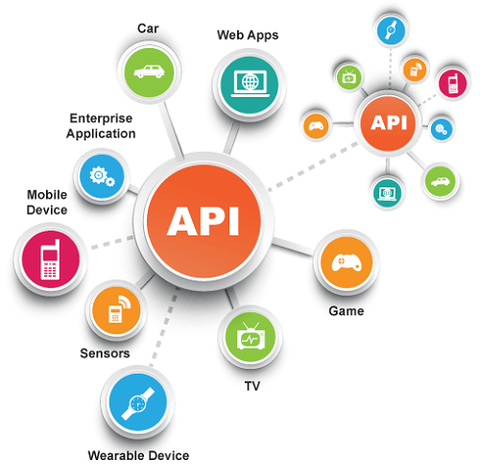
Application Programming Interfaces, commonly known as APIs, are an important part of modern software development. They allow different applications, systems and services to communicate with each other using defined rules and data formats.
API software can help organizations create, manage, secure, monitor and document these connections. APIs are widely used in SaaS applications, mobile apps, websites, enterprise software, payment systems, cloud platforms and other digital environments.
Understanding API types, architecture, authentication, security and integration methods is useful for anyone working with modern software systems.
What Is API Software?
API software refers to tools, platforms and technologies used to create, manage, test, document, secure and monitor APIs.
An API acts as an interface between software components. Instead of requiring one application to understand the internal implementation of another system, the API provides defined operations that can be requested through specific endpoints or methods.
For example, an application might use an API to:
Retrieve customer information
Submit an order
Send notifications
Process data
Authenticate users
Access cloud resources
Retrieve analytics
Connect with another SaaS application
API software can therefore simplify communication between different applications and services.
How APIs Work
A typical API interaction involves several components:
A client sends a request.
The API receives and processes the request.
The API communicates with the relevant application or database.
The server processes the requested operation.
A response is returned to the client.
A request may contain information such as an endpoint, HTTP method, authentication credentials, parameters and data.
The response commonly contains a status code and structured data.
Common API Types
APIs can be categorized in several ways.
REST APIs
Representational State Transfer (REST) is one of the most widely used approaches for web APIs.
REST APIs commonly use HTTP methods such as:
GET — retrieve information
POST — create or submit information
PUT — replace or update information
PATCH — partially update information
DELETE — remove information
REST APIs frequently use JSON for data exchange.
SOAP APIs
Simple Object Access Protocol (SOAP) is a protocol-based approach that commonly uses XML for structured messaging.
SOAP can be found in enterprise environments where formal standards, structured contracts and established security mechanisms are important.
GraphQL APIs
GraphQL allows clients to request specific data fields rather than receiving a fixed response structure.
It can be useful when applications need flexible data retrieval from complex systems.
WebSocket APIs
WebSocket technology supports persistent, two-way communication between a client and server.
It can be useful for applications requiring real-time updates, such as:
Live dashboards
Messaging
Collaboration systems
Real-time notifications
Internal APIs
Internal APIs are designed primarily for communication between components within an organization.
They can connect internal applications, databases, microservices and business systems.
External APIs
External APIs are made available to third-party developers or external applications under defined access rules.
They are commonly used to connect external applications with platforms and digital services.
Important API Features
API software commonly includes several capabilities.
API Management
API management platforms can help organizations manage API access, traffic, policies, analytics and lifecycle activities.
Typical functions include:
API publishing
Access management
Traffic control
Usage monitoring
Version management
Developer access
API Documentation
Documentation explains how developers can interact with an API.
Good documentation commonly includes:
Endpoints
HTTP methods
Parameters
Authentication requirements
Request examples
Response examples
Error codes
Data formats
OpenAPI is a widely used specification for describing HTTP APIs.
API Testing
API testing verifies whether endpoints behave as expected.
Testing can examine:
Request handling
Response data
Authentication
Error conditions
Performance
Data validation
Authorization
Tools used for API testing may support manual requests, automated test collections and test environments.
API Integration
API integration connects two or more software systems through APIs.
For example, a SaaS application may integrate with:
Customer relationship management platforms
Enterprise resource planning systems
Payment platforms
Email systems
Analytics tools
Cloud storage
Communication platforms
Identity providers
API integration can reduce the need for manually transferring information between systems.
API Authentication
Authentication determines whether an API request comes from an identified client or user.
Common authentication approaches include:
API Keys
An API key is a value provided to identify an application or integration.
API keys are relatively simple but should be protected and managed carefully.
OAuth
OAuth allows applications to obtain authorized access without requiring the user to provide their primary credentials directly to the requesting application.
It is widely used for delegated authorization.
JSON Web Tokens
JSON Web Tokens (JWTs) can carry claims between systems and are commonly used in authentication and authorization workflows.
The appropriate authentication approach depends on the API architecture and security requirements.
API Security
API security is essential because APIs can expose application functionality and data.
Important security practices include:
HTTPS
APIs should generally use encrypted HTTPS connections to protect information while it travels between systems.
Authentication and Authorization
Authentication identifies the requester, while authorization determines what that requester is permitted to access.
These controls should be designed separately and applied according to the application's requirements.
Input Validation
APIs should validate incoming data to reduce the risk of malformed or unexpected requests.
Rate Limiting
Rate limiting controls how frequently a client can make requests within a specific period.
It can help protect APIs from excessive traffic and certain types of abuse.
Access Controls
Access policies should ensure that users and applications can access only the resources they are authorized to use.
Secure Credential Management
API keys, tokens and other credentials should not be unnecessarily exposed in source code, public repositories or client-side applications.
API Gateway
An API gateway acts as an entry point between clients and backend services.
It can perform functions such as:
Request routing
Authentication
Rate limiting
Traffic management
Logging
Request transformation
Access policies
API gateways are particularly useful in architectures containing multiple backend services.
API Versioning
APIs may evolve over time as applications change.
Versioning allows developers to introduce changes while maintaining compatibility with existing clients.
Common approaches include:
URL versioning
Header-based versioning
Query-parameter versioning
For example, an API might distinguish between different versions using paths such as /v1/ and /v2/.
A clear versioning strategy can reduce disruption when APIs change.
API Error Handling
APIs should provide meaningful responses when requests cannot be processed.
Common HTTP status codes include:
| Status Code | General Meaning |
|---|---|
| 200 | Successful request |
| 201 | Resource created |
| 400 | Invalid request |
| 401 | Authentication required or invalid |
| 403 | Access not permitted |
| 404 | Resource not found |
| 429 | Too many requests |
| 500 | Server-side error |
Consistent error structures make APIs easier for developers to troubleshoot and integrate.
API Data Formats
APIs can exchange information using different data formats.
JSON
JSON is widely used in modern web APIs because it is relatively compact and easy for many programming languages to process.
XML
XML provides a structured format and remains common in some enterprise and SOAP-based environments.
Form Data
Form-based formats can be used when applications submit structured form information or upload files.
The appropriate format depends on the API design and integration requirements.
API Monitoring and Analytics
API monitoring helps teams understand how APIs behave in production.
Important measurements can include:
Request volume
Response time
Error rate
Availability
Traffic patterns
Authentication failures
Rate-limit events
Analytics can also help identify frequently used endpoints and unusual traffic patterns.
API Integration Architecture
API integrations can be designed using different architectural approaches.
Point-to-Point Integration
One application communicates directly with another application.
This can be simple for a small number of systems but may become difficult to manage as integrations increase.
API-Led Architecture
API-led approaches organize APIs into reusable layers.
These may include:
System APIs
Process APIs
Experience APIs
The exact implementation varies between organizations.
Event-Driven Integration
Event-driven systems respond to events generated by applications or services.
For example, an order-created event could trigger inventory processing, notification workflows and analytics updates.
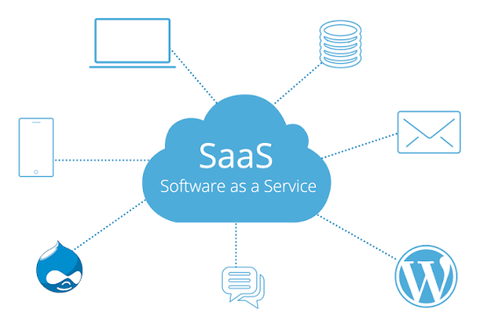
APIs in SaaS Applications
APIs are particularly important in SaaS environments.
A SaaS platform may expose APIs for:
User management
Account information
Data access
Reporting
Billing integration
Workflow automation
Third-party applications
APIs also allow SaaS products to connect with other platforms without requiring direct access to their internal databases.
API Development Lifecycle
API development generally involves several stages:
Requirements analysis
API design
Data-model planning
Development
Authentication and security implementation
Testing
Documentation
Deployment
Monitoring
Versioning and maintenance
A well-defined lifecycle helps maintain consistency as APIs evolve.
Benefits of API Software
API software and management tools can provide several advantages:
Application connectivity
Reusable integrations
Automated data exchange
Easier third-party integration
Centralized API management
Improved monitoring
Structured security controls
Developer documentation
Better integration visibility
Support for scalable software architectures
The actual benefits depend on API design, implementation quality and the surrounding application architecture.
Common API Challenges
API implementations can also introduce technical challenges.
Security Risks
Poorly protected endpoints or credentials can expose applications and data.
Version Compatibility
Changes to API structures can affect existing applications.
Rate Limits
High-volume integrations may encounter request limits.
Data Consistency
Multiple systems exchanging information can create synchronization challenges.
Documentation Gaps
Incomplete documentation can make APIs difficult to integrate and maintain.
Monitoring Complexity
Large API environments may contain hundreds or thousands of endpoints, making centralized monitoring important.
Important API Development Practices
A reliable API implementation commonly considers:
Consistent endpoint naming
Clear documentation
Secure authentication
Strong authorization
Input validation
HTTPS
Rate limiting
Structured error responses
API versioning
Automated testing
Monitoring and logging
Appropriate data minimization
Backward compatibility where required
Security and performance should be considered during API design rather than added only after development.
Frequently Asked Questions
What is API software?
API software refers to tools and technologies used to develop, manage, test, secure, document and monitor application programming interfaces.
What is the most common type of web API?
REST is one of the most widely used approaches for web APIs, although GraphQL, SOAP and other technologies are also used for different requirements.
What is API integration?
API integration connects different software applications through defined API interfaces so they can exchange information or trigger operations.
What is an API gateway?
An API gateway provides a centralized entry point for API requests and can handle routing, authentication, traffic management, rate limiting and other policies.
Why is API security important?
APIs can provide access to application functionality and data. Security controls help prevent unauthorized access and reduce risks associated with exposed interfaces.
Are APIs used in SaaS applications?
Yes. APIs are widely used by SaaS applications to connect with users, third-party applications, internal services, databases and external platforms.
Conclusion
APIs provide a structured way for software applications and services to communicate. API software extends this concept by providing tools for API development, integration, testing, documentation, security, monitoring and lifecycle management.
REST, SOAP, GraphQL and WebSocket APIs support different communication requirements, while technologies such as API gateways, OAuth, API keys, JSON, OpenAPI and rate limiting help build and manage API environments.
For modern SaaS and enterprise applications, a well-designed API strategy can improve application connectivity, automation and interoperability. At the same time, security, documentation, versioning, monitoring and error handling remain important considerations throughout the API lifecycle.
Disclaimer: This article is provided for general informational and educational purposes only. API technologies, security practices, software platforms and technical standards can change over time. Developers and organizations should consult current technical documentation and applicable security guidance before implementing APIs in production environments. This article does not promote or recommend any particular API software, platform or technology.
Related Post...
SaaS Application Development Guide: Explore Architecture, Development, Features, Security & Scalability
Updated: September 22, 2026
Read More
IVF Treatment Risks Guide: Explore Potential Complications, Side Effects & Important Considerations
Updated: September 22, 2026
Read More