API Management Guide: Business Integrations, Application Security, and Digital Operations
API management helps organizations create, publish, secure, monitor, and govern application programming interfaces, commonly known as APIs.
APIs allow different applications and systems to exchange data and functionality. They are widely used to connect enterprise software, cloud applications, mobile applications, customer platforms, payment systems, databases, and external business partners.
An API management platform can provide a centralized layer for controlling how APIs are accessed, monitored, secured, documented, and integrated into broader digital operations.
Why API Management Matters
Modern organizations often operate many applications across cloud, on-premises, and hybrid environments.
Without centralized API governance, teams can encounter challenges involving:
API security
Duplicate integrations
Inconsistent authentication
Limited visibility
Uncontrolled API access
Version-management issues
Performance problems
Data-governance concerns
Difficult troubleshooting
API management can help establish common controls across an organization's API environment.
What Is API Management?
API management is a collection of technologies and processes used to manage APIs throughout their lifecycle.
A typical API management environment can include:
API gateways
API publishing
Authentication
Authorization
Traffic management
Rate limiting
API analytics
Developer portals
API documentation
Version control
Access policies
Monitoring
Lifecycle governance
The exact capabilities depend on the platform and implementation.
API Gateways
An API gateway commonly acts as an intermediary between API consumers and backend applications.
A simplified architecture can look like:
Application → API Gateway → Business Application → Database or External System
The gateway can apply policies before requests reach backend systems.
Potential gateway functions include:
Request routing
Authentication
Authorization
Rate limiting
Traffic control
Request transformation
Response transformation
Logging
Monitoring
Security policy enforcement
This centralized layer can make it easier to apply consistent API policies across multiple applications.
API Security
API security is an important part of API management because APIs can expose business data and application functionality.
Security controls may include:
Authentication
Authorization
API keys
OAuth
OpenID Connect
Mutual TLS
Token validation
Encryption
Rate limiting
Threat detection
Access logging
Credential management
Security requirements should be based on the sensitivity of the data, application architecture, users, business processes, and applicable regulations.
Authentication and Authorization
Authentication determines whether a user, application, or system can establish its identity.
Authorization determines what that authenticated entity is permitted to access.
Common API security technologies include:
OAuth 2.0
OpenID Connect
JSON Web Tokens
API keys
Mutual TLS
Identity-provider integration
Organizations should avoid treating authentication alone as sufficient security. Authorization, access controls, monitoring, and appropriate application-level protections are also important.
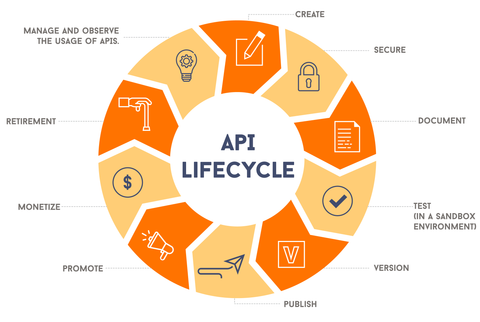
API Lifecycle Management
APIs generally move through several stages.
A typical lifecycle includes:
Design → Develop → Test → Publish → Monitor → Version → Retire
API lifecycle management can help organizations maintain consistency as APIs evolve.
Important lifecycle activities may include:
API design
Documentation
Testing
Security review
Deployment
Version management
Monitoring
Deprecation
Retirement
Clear lifecycle processes can reduce confusion when multiple applications depend on the same API.
API Governance
API governance establishes standards for how APIs are designed, secured, documented, and maintained.
Governance policies may address:
API naming
Data formats
Authentication
Authorization
Versioning
Documentation
Error handling
Security testing
Data classification
Logging
Retention
Deprecation
Governance can help different development teams follow consistent practices across an enterprise.
API Integration for Business Systems
APIs can connect many types of business applications.
Common integrations include:
Enterprise resource planning systems
Customer relationship management platforms
Payment systems
Accounting platforms
Human resources systems
E-commerce platforms
Inventory systems
Supply-chain platforms
Data warehouses
Business intelligence platforms
Customer applications
For example, an e-commerce application may use APIs to communicate with inventory, payment, customer, shipping, and financial systems.
API Management and Digital Transformation
Digital transformation often requires organizations to connect existing systems with newer applications and cloud technologies.
API management can provide an integration layer between legacy systems and modern applications.
For example:
Legacy System → API Layer → Cloud Application → Mobile or Web Application
This approach can allow organizations to expose selected functionality without directly connecting every application to every backend system.
API Analytics and Monitoring
API analytics can provide visibility into application traffic and system performance.
Organizations may monitor:
API requests
Response times
Error rates
Traffic volume
Authentication failures
Geographic activity
Consumer applications
Endpoint usage
Rate-limit events
Availability
Monitoring can help identify unusual behavior, performance bottlenecks, integration problems, and underused APIs.
API Rate Limiting
Rate limiting controls how frequently a user, application, or client can make API requests.
It can help organizations:
Protect backend systems
Manage traffic spikes
Reduce excessive requests
Support predictable performance
Control resource consumption
Rate limits can be based on users, applications, API keys, subscription plans, endpoints, or other business rules.
Appropriate limits depend on application requirements and expected traffic.
API Versioning
APIs can change over time as applications evolve.
Versioning helps organizations manage these changes while maintaining compatibility with existing applications.
Common approaches include:
URL-based versioning
Header-based versioning
Query-parameter versioning
Organizations should establish clear policies for API updates, backward compatibility, deprecation periods, and migration procedures.
Developer Portals
Developer portals provide documentation and tools for people or organizations that use APIs.
A portal may include:
API documentation
Endpoint information
Authentication instructions
Usage guidelines
Code examples
API keys or credentials
Testing tools
Version information
Usage analytics
Developer portals can help internal and external API consumers understand how an API should be used.
API Monetization and Business Models
Some organizations expose APIs to external customers, partners, or developers as part of their broader digital strategy.
API programs can support different business models, including:
Partner integrations
Developer ecosystems
Digital platforms
Embedded functionality
Data access
Application partnerships
Organizations should establish appropriate access, security, contractual, and usage policies when APIs are made available outside the internal environment.
API Management and Cloud Computing
Cloud environments have increased the number of applications and services that communicate through APIs.
API management platforms may operate across:
Public cloud
Private cloud
Hybrid environments
On-premises infrastructure
Multi-cloud environments
Centralized API policies can help organizations manage application connectivity across different infrastructure environments.
Automation and Artificial Intelligence
AI and automation can increasingly support API operations.
Potential applications include:
API anomaly detection
Automated documentation
Traffic analysis
Security monitoring
API testing
Error classification
Performance analysis
Automated policy recommendations
Intelligent troubleshooting
AI-generated recommendations should be validated before being applied to security-sensitive or production environments.
API Data Governance
APIs frequently transmit business and customer information, making data governance important.
Organizations should define controls for:
Data classification
Data access
Data minimization
Data retention
Data encryption
Logging
Data lineage
Privacy
Third-party access
API policies should align with the organization's broader data-governance framework.
API Management Implementation
Organizations evaluating API management can follow a structured process.
1. Inventory existing APIs
Identify current APIs, applications, owners, consumers, and dependencies.
2. Classify APIs
Determine whether APIs are internal, partner-facing, or externally accessible.
3. Define security requirements
Establish authentication, authorization, encryption, monitoring, and access policies.
4. Establish governance
Define API design, documentation, versioning, testing, and lifecycle standards.
5. Select management capabilities
Evaluate gateway, analytics, developer portal, monitoring, security, and integration capabilities.
6. Connect business systems
Prioritize important enterprise applications and integration workflows.
7. Monitor production APIs
Track traffic, errors, latency, security events, and usage patterns.
API Management Planning Checklist
Organizations evaluating API management technology can consider:
Inventory existing APIs
Identify API owners
Classify API consumers
Define authentication requirements
Establish authorization policies
Review API gateway requirements
Define rate-limiting policies
Establish versioning standards
Review API documentation
Evaluate developer portal capabilities
Define monitoring requirements
Establish API analytics
Review data-governance requirements
Assess cybersecurity controls
Define API lifecycle procedures
Establish deprecation policies
Test security and performance
Document integration dependencies
Recent Developments in API Management
API management continues to evolve alongside cloud computing, distributed applications, AI, and digital business platforms.
Important developments include:
Cloud-native API management
API security automation
AI-assisted API operations
Automated API discovery
Advanced API analytics
Zero-trust integration
API observability
Multi-cloud API governance
Event-driven architectures
Greater integration between APIs and AI applications
Organizations are also paying greater attention to API inventories and shadow APIs as application environments become more complex.
Laws, Policies, and Compliance Considerations
API environments can be affected by requirements involving:
Data protection
Privacy
Cybersecurity
Financial information
Healthcare information
Payment data
Consumer protection
Industry-specific regulations
Record retention
Third-party data access
The applicable requirements vary according to the data involved, organization, industry, jurisdiction, and API architecture.
Organizations should review API data flows as part of broader privacy and security assessments.
Tools and Resources
Organizations researching API management can review:
API gateway platforms
API management platforms
API documentation tools
API testing tools
Identity and access-management platforms
Cloud integration platforms
API analytics systems
Application monitoring tools
Data-governance frameworks
Cybersecurity frameworks
FAQs
1. What is API management?
API management is the process and technology used to create, secure, publish, monitor, govern, and manage APIs throughout their lifecycle.
2. What does an API management platform do?
Depending on the platform, it can provide API gateways, authentication, authorization, rate limiting, analytics, monitoring, documentation, developer portals, and lifecycle management.
3. What is an API gateway?
An API gateway acts as an intermediary between API consumers and backend applications. It can route requests and apply security, traffic-management, and monitoring policies.
4. How does API management improve application security?
API management can centralize controls such as authentication, authorization, encryption, rate limiting, monitoring, and access policies. It does not replace secure application development or other cybersecurity controls.
5. Can API management support cloud and enterprise integrations?
Yes. API management can connect cloud applications, enterprise systems, partner platforms, mobile applications, and other digital systems. The specific integration capabilities depend on the technology architecture.
Conclusion
API management provides a structured way to manage the connectivity between applications, business systems, cloud platforms, and external partners.
A comprehensive API program combines security, governance, lifecycle management, monitoring, analytics, documentation, and integration controls.
Organizations evaluating API management should consider their application architecture, API inventory, security requirements, integration priorities, data governance, monitoring needs, and long-term digital strategy.
Related Post...
API Management Guide: Business Integrations, Application Security, and Digital Operations
Updated: September 23, 2026
Read More
Document Workflow Automation Guide: Approvals, Records, and Business Processes
Updated: September 23, 2026
Read More
Project Portfolio Management Guide: Project Priorities, Resources, and Business Planning
Updated: September 23, 2026
Read More